Your Uncommonly Amazing WordPress Tech Partner
For associations, publishers and training providers

WordPress SSO Integration for Membership Sites and LMS

Your members already have a login at their university, employer or another platform. A WordPress SSO integration lets them use it on your site, with the right access waiting for them. We build it and can look after it afterward.

Founded 2014, trusted by 100+ membership sites
Free Movement logo

We took Free Movement’s university single sign-on (OpenAthens) live in under two months, and the case study reports that OpenAthens said projects like it typically take under a year.

Read the case study or OpenAthens’ own write-up of the project.
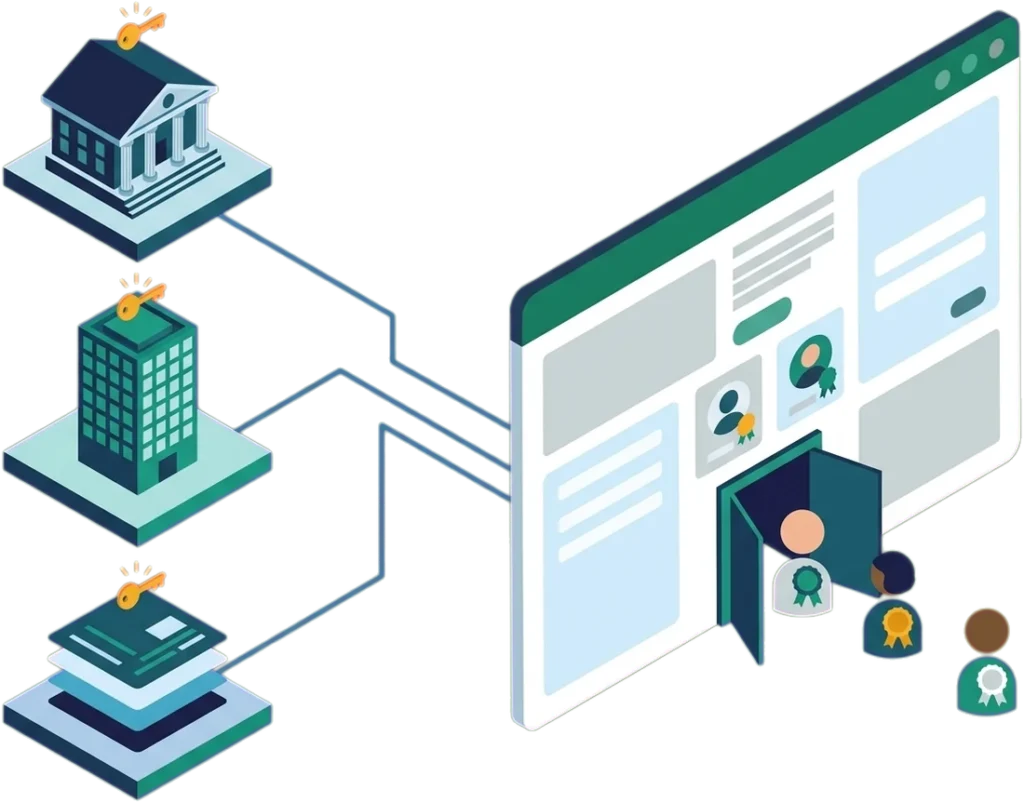
Illustration of members from a university, an employer and a partner platform entering one membership site through a single login gate

SSO providers we can connect to WordPress

We can also connect WordPress to other SAML 2.0 or OpenID Connect identity providers.

  • miniOrange
  • Microsoft Entra ID
  • Okta
  • Google Workspace
  • Auth0
  • Ping Identity
  • Keycloak
  • JumpCloud

Product names and logos are trademarks of their owners, and Shibboleth® is a registered trademark of Internet2. We list them to show which providers we can connect WordPress to. Being listed here doesn’t mean a provider endorses or partners with MemberFix.
As seen on
LearnDash logo
Membership Geeks logo
WP Fusion logo
MemberPress logo
MemberMouse logo
Membership Academy logo

What WordPress SSO integration means for a membership business

WordPress SSO integration lets a person sign in with an account they already have somewhere else, such as their university, their employer or another platform, and arrive on your membership site as a recognized member with the right access. In SAML 2.0, the member’s identity provider checks who they are and sends your site a signed statement about them. In the OASIS SAML technical overview’s words, the identity provider “issues a SAML assertion representing the user’s logon security context.” OpenID Connect, in its Core specification’s words, is “a simple identity layer on top of the OAuth 2.0” protocol.

The handshake is only part of the work. The rest is what happens after it: is this person already a member, which level do they get, which courses open, and who creates the account if none exists? A plugin can get the handshake working. The answers are rules specific to your business, and that is where the project work sits.

A plugin’s setup guide may be all you need to sign staff in to one internal tool. This page is for members who arrive from many organizations, where what they see depends on which one.

How a login becomes a membership level

How a login becomes a membership levelDiagram of a sign-in started on a membership site: the member is sent to their identity provider, the identity provider returns a signed statement, WordPress finds, links or creates the account, and the attributes, where the provider releases them, set the membership levelMemberChooses to sign inwith theirinstitution,employer orplatformIdentityproviderTheir university,employer or otherplatform. Checkswho they are.YourWordPress siteFinds, links orcreates theaccountMembershiplevelLevel, role orcourse accessSet by your rulesSent tosign inSigned statement(attributes if released)Attributes mappedto accessStandard handshake: SAML 2.0 or OpenID ConnectThe membership layer: where the project work sitsHow a login becomes a membership levelDiagram of a sign-in started on a membership site: the member is sent to their identity provider, the identity provider returns a signed statement, WordPress finds, links or creates the account, and the attributes, where the provider releases them, set the membership levelMemberChooses to sign in with theirinstitution, employer or platformStandard handshakeIdentity providerTheir university, employer or otherplatform. Checks who they are.SAML 2.0 or OpenID ConnectYour WordPress siteFinds, links or creates the accountThe membership layerMembership levelLevel, role or course accessSet by your rulesSent to sign inSigned statement(attributes if released)Attributes mappedto access
  1. A member opens your site and chooses to sign in with their institution, employer or platform.
  2. Your site sends them to their identity provider, which checks who they are.
  3. The identity provider sends back a signed statement about the person, which can include attributes such as their organization or group, depending on what the provider releases.
  4. WordPress finds the matching account, links it to an existing one, or creates it.
  5. Those attributes, where they arrive, decide the membership level, role or course access.

Steps 1 to 3 are the standard handshake, and SAML 2.0 and OpenID Connect each do it in their own way. Steps 4 and 5 are your rules, and they take the design work.

Who this is for, and who it isn’t

A good fit if

Not a fit if

What we’ve shipped

Free Movement: university single sign-on

University single sign-on (OpenAthens) live in under two months. The case study reports that OpenAthens said such projects typically take under a year. The project used OpenAthens Keystone, connected to WordPress over OpenID Connect.

TechServe Alliance: one login for the main site and the community

TechServe Alliance’s BuddyBoss community is a second WordPress site next to their main site. A user-sync plugin connects the two, so members who log in on the main site are already signed in when they open the community, and only people with the member role get in. For members it works like SSO, without an identity provider in the middle. We also fixed a login loop: a member who can’t get into the community now lands back on the main site instead of being caught in the loop.

Invision Community forums on WordPress logins

Since 2018, several of our clients have run an Invision Community forum next to their WordPress site. Their members sign in to the forum with their WordPress account, through a WordPress-to-Invision bridge plugin that replaces the forum’s own login. We have upgraded and supported these setups, and published what we learned: our setup guide and why a WordPress admin can’t see Invision’s Block Manager.

Looking after it: we also keep live sign-ins working on the sites we look after. When a client forwarded a miniOrange notice that their SAML certificate was about to expire, we checked it against their setup, confirmed their logins would keep working, and scheduled the plugin update with a rollback point. On another site, we warned the client that the license on their SSO plugin was about to run out.
Memberium Certified Agency Partner badge
MemberPress Certified Developer badge
Keap Certified Partner Badge

What an SSO project covers

Every project differs. This is what we scope with you before building.

SAML 2.0 and OpenID Connect connections

Your WordPress site has to talk to the identity provider on the other side, whether that is a university federation, an employer’s identity system or another platform. If the choice between SAML and OpenID Connect is open, we explain the trade-off (table below).

OpenAthens

OpenAthens documents more than one route for a publisher. You can integrate through your own SAML service provider, with Shibboleth or SimpleSAMLphp. For products without one, OpenAthens Keystone is a cloud-hosted service that connects to your platform with an OpenID Connect library and takes care of the SAML requirements. Free Movement’s project used Keystone, connected to WordPress over OpenID Connect. Choosing between the routes is part of the scope.

Mapping the login to a membership level

The identity provider can send attributes such as an organization, a group or a role, depending on what it releases. The project decides what each one grants on your site: a membership level, a WordPress role, a course group. That mapping has to end up wherever access is held today, whether that is a membership plugin such as MemberPress or CRM tags through WP Fusion.

Account creation: at first login, in advance, or by linking

Who creates the account decides what you can do before someone’s first login. The table below compares the three patterns.

Institution-level access without per-user seats

When a university or a company buys access for everyone, you don’t want a separate seat to manage for each person. The project defines access that belongs to the organization, and who on your staff adds or changes an organization. Where the rules need custom code, that is plugin development.

Testing provisioning before launch

OpenAthens’ own write-up of the project advises that it is “worth investing time to thoroughly test” user provisioning, because “some of WordPress’s default configurations need adjusting to meet the OpenAthens Federation’s requirements.” Our pre-launch QA covers plugin conflicts, security, user experience, functionality and performance. Which test accounts each kind of visitor needs is something we settle in the scope.

SAML, OpenID Connect and OpenAthens: how they relate

OptionWhat it isFits when
SAML 2.0The identity provider sends your site a signed assertion about the person (OASIS SAML 2.0 technical overview).The organization on the other side runs a SAML identity provider. OpenAthens expects most of a publisher’s customers or subscribers to have one.
OpenID ConnectA “simple identity layer on top of the OAuth 2.0” protocol (OpenID Connect Core 1.0).The other side offers OpenID Connect, or you use OpenAthens Keystone, which connects over it.
OpenAthens, through a federation or 1:1A way to connect, not a separate protocol. OpenAthens helps service providers integrate using SAML, and its 1:1 connections can link SAML-enabled systems “without needing to join a federation.”Your buyers are universities and libraries that already use OpenAthens, or you want to connect to individual organizations directly.

Source note: protocol descriptions from the OASIS SAML 2.0 technical overview, the OpenID Connect Core specification and OpenAthens’ service provider integrations page. The “fits when” column is our view.

Who creates the member’s account?

SSO signs a person in. It does not always create their account, and that changes what you can do before their first login. Three patterns come up.

OptionHow it worksGood whenWatch for
Create at first loginA new WordPress account is created when the person first signs in through SSO, if none exists.Anyone from a trusted organization may join, and the identity provider sends everything you need at login.No WordPress account exists to email or assign before first login.
Create in advanceThe other platform or your system creates the account before the person ever signs in, through SCIM or an API call.The other platform owns the user list, or the member record (tags, enrollments, billing) must exist first.Needs work on both sides and agreement on who owns each field.
Link to an existing accountThe login is matched to an account you already have, using a matching rule you agree on, such as email or username.Your members already have accounts.A member whose institution email differs from the one on file can end up with a second account, so check that the matching field is one you can trust before linking automatically.

Source note: plugin behavior is from the miniOrange and WP SAML Auth pages on WordPress.org (both create an account on first login, and miniOrange links accounts by username or email); SCIM is described in Okta’s documentation as “a defined schema for representing users and groups, and a RESTful API to run CRUD operations on those user and group resources.” “Good when” and “watch for” are our view.

Two checks on the other platform’s side

  • Does it need each user to exist before they can sign in? If so, the account has to be created there too, for example by an API call.
  • Does it depend on a field, such as a company name, being present on every account? If so, that field should be required and locked on your side.

Where off-the-shelf SSO plugins fit

Plugins are a real option. Two you will see in search results:

miniOrange SAML Single Sign-On

Its WordPress.org page says it makes your WordPress site “function as a SAML-compliant Service Provider (SP) by using the SAML 2.0 protocol.” The page describes account creation on first login, account linking by username or email, and assigning WordPress roles from Administrator to Subscriber. It also lists SCIM provisioning, federation sign-in for universities and integrations with LearnDash, WooCommerce, BuddyPress, MemberPress and Paid Memberships Pro. Check which of those your edition includes before you rely on one.

WP SAML Auth

Per its WordPress.org page, “a new WordPress user will be created if none exists (although this behavior can be disabled).”

Our view: a plugin can get the handshake working. You need a project when the plugin has no setting for your access rules, when access belongs to an organization instead of a person, or when the account has to exist on another platform too.

How an SSO project runs

  1. Tell us how members log in today

    Use the form below. Tell us who your members are, which organizations they come from and what you have in place.

  2. Audit first

    The free audit is an outside-in first look. SSO touches the login and the access rules behind it, so for a deeper technical look before we plan, a paid audit, from $1,000, covers it.

  3. A plan on the tools you already own

    We build the plan around your membership plugin, your CRM and the identity providers you already deal with, and we recommend a migration only when it is the right call.

  4. Build and test

    Before launch, our QA covers plugin conflicts, security, user experience, functionality and performance.

  5. Look after it

    Afterward you can keep us on through Managed TechOps: one team for development, support, hosting, troubleshooting and planning, month to month. Updates and regression tests are included. You keep everything if you leave.

What drives the cost: we don’t publish SSO prices, because two projects rarely match. It depends on how many identity providers and organizations are involved, whether accounts are created at login or in advance, how many membership levels the login maps to, which systems on the other side we connect to, and how much you want us to look after afterward. We’ll tell you what your project would take before any building begins.

Six questions we ask before an SSO project

  1. Which identity provider or providers will members arrive from, and who on that side can configure them?
  2. Which attributes does each one send, and do they include what decides access (organization, group, role)?
  3. Who owns the user record, your site or the other platform?
  4. How do those attributes map to membership levels, roles or courses?
  5. Who adds a new organization, and how?
  6. When someone leaves an organization, or its subscription ends, what removes their access, and what happens to a session that is already signed in?

Who you'd work with

Our team plans, builds and supports your site. See who does what (opens in a new tab)
  • Vic Dorfman, Founder and CEO at MemberFixVic
  • Costi Muresanu, Head of Operations at MemberFixCosti
  • Risto Karaivanov, Head of Technical Sales at MemberFixRisto
  • Lesly Garreau, Head of AI at MemberFixLesly
  • Trim Qemali, Senior Developer at MemberFixTrim
  • Denys Melnychuk, Senior Developer at MemberFixDenys
  • Elizabeth Lukanova, Senior Developer at MemberFixElizabeth
  • Edin Čičkušić, Senior Developer at MemberFixEdin
  • Dejan Biberovic, Senior Developer at MemberFixDejan
  • Bane Mladenovic, Maintenance, Testing, QA at MemberFixBane
  • Bojan Pavlovic, Senior Developer at MemberFixBojan
  • Dafina Cvetanovska, Head of People at MemberFixDafina
  • Milos Veselinovic, Tech Project Manager at MemberFixMilos
  • Yana Shvets, Marketing and Content at MemberFixYana
  • Denny Cave, CTO at MemberHostDenny
  • Milan Maksimovic, Support at MemberHostMilan

*Denny and Milan work at MemberHost, our sister company.
SOME OF THE AWESOME FOLKS WE’VE WORKED WITH
ProcessDriven logo
Paul Wilson Golf logo
Splasheo logo
Nomad Capitalist logo
Echelon Front logo
AuthorityHacker logo
SSO integration

How should your members be able to log in?

Tell us who your members are, where their logins live today and what they need access to. A technical team member will tell you what we'd do.

✓ Book a chat, or just get a reply within one business day
✓ Talk to an expert who helps first, not a hard sell
✓ Trusted by 100+ membership sites
Trusted by teams using
LearnDash MemberPress WP Fusion WooCommerce BuddyBoss Paid Memberships Pro FunnelKit GamiPress Gravity Forms

WordPress SSO integration FAQ

Do we need custom development, or will an SSO plugin do?

A plugin may do if the sign-in is the whole job. Custom work may be needed when a plugin cannot express your organization-based access rules, or when accounts must also exist on another platform. We tell you which case you are in before we quote.

Should we use SAML or OpenID Connect?

It depends on what the other side offers. OpenAthens says it supports the SAML 2.0 protocol for single sign-on for library patrons, and its Keystone service connects to a publisher’s platform through an OpenID Connect library. If both are on the table, we explain the trade-off for your setup in plain English.

Does SSO create our members’ accounts?

Not by itself. Depending on the setup, the account is created at first login, created in advance through SCIM or an API call, or linked to one you already have. The table above covers the trade-offs, and we help you pick one before building.

Can members from several organizations log in to one site, each with the right access?

That is what this page is for. We first check which attributes your identity providers release, then define how each organization’s attributes map to the right level and plan the testing for each kind of visitor before launch.

How long does it take, and what does it cost?

Free Movement’s university single sign-on (OpenAthens) went live in under two months, and the case study reports that OpenAthens said such projects typically take under a year. Your timeline depends on how many identity providers are involved, how access maps and what the other side has to configure. We don’t publish SSO prices. A paid audit starts from $1,000 if you want a deeper look first, and we scope the build after we hear your setup.

What happens after launch?

You can keep us on through Managed TechOps, month to month, with updates and regression tests included. You keep everything if you leave. If you run an association, see also our association website design work.

Vic DorfmanWritten and reviewed by Vic Dorfman, founder of MemberFix. Founded in 2014, MemberFix is the WordPress tech team for established membership, e-learning, association and online community businesses. Last reviewed: October 2026.